SaaS & Technology Companies
Build customer trust and accelerate enterprise growth with scalable security and compliance.
Explore ResourcesTSEC enables technology-driven organizations to build and operationalize governance, security, and compliance foundations—accelerating SOC 2 and NYDFS readiness with a modern, tech-enabled approach.
From high-growth technology companies to regulated enterprises, TSEC helps organizations turn cybersecurity, compliance, and risk into a competitive advantage.
Build customer trust and accelerate enterprise growth with scalable security and compliance.
Explore Resources
Strengthen regulatory readiness, cyber risk management, and customer confidence.
Explore Resources
Protect sensitive data while building scalable security and compliance programs.
Explore Resources
Establish a stronger security posture and demonstrate compliance to clients and strategic partners.
Explore Resources
Build compliance into your growth strategy before security and regulatory requirements become a barrier.
Explore Resources
Modernize GRC operations with continuous monitoring, control intelligence, and compliance automation.
Explore ResourcesIntegrated technology, cybersecurity expertise, and governance leadership to help organizations reduce risk, meet regulatory requirements, strengthen resilience, and grow with confidence.
End-to-end automation for SOC 2, NYDFS, ISO 27001, and other regulatory frameworks — streamlining evidence collection, policy generation, control monitoring, and compliance workflows.
Explore Compliance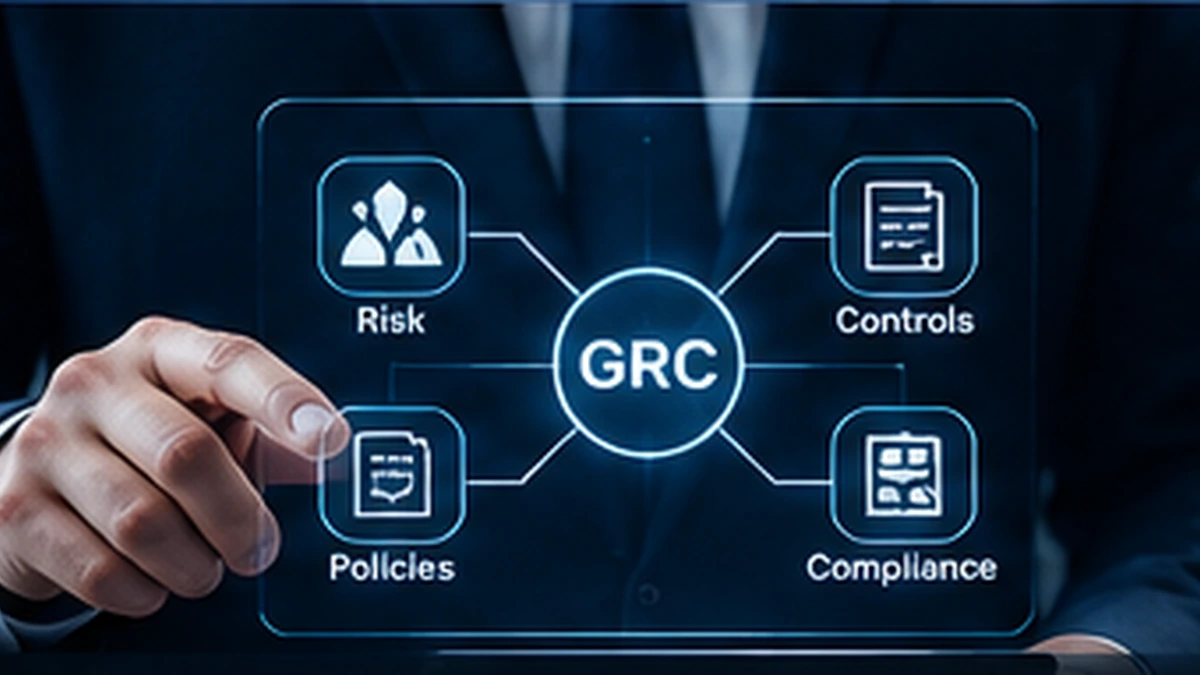
AI-assisted GRC intelligence that connects risks, controls, policies, and regulatory requirements — providing continuous visibility across your security and compliance environment.
Explore Risk Management
Ongoing cybersecurity, risk, and compliance leadership for growing and regulated organizations — combining strategic oversight, risk management, audit readiness, and executive advisory.
Explore Fractional vCISO
Enterprise-grade risk and governance frameworks aligned with business objectives, regulatory obligations, and organizational risk — including risk assessments, policy architecture, control structures, and governance models.
Explore GovernanceWe help organizations meet global standards and regulatory requirements with confidence, security and peace of mind.
Information Security
Information Security Management System • Global standard for information security
Cybersecurity Framework
Identify, Protect, Detect, Respond • Recover
Part 500
Cybersecurity requirements • Covered financial entities
Trust Services Criteria
Security, availability, processing integrity, confidentiality • privacy
Health Data Security
Protection of electronic protected health information • ePHI
Anti-Money Laundering
Customer due diligence • Financial crime risk management
Business Continuity
Business Continuity Management System • Organizational resilience
IT Governance
Enterprise IT governance • Information & technology management
AI Management System
Responsible AI governance • Risk management & lifecycle controls
Payment Card Security
Payment card data protection • Cardholder data environment
AI Risk Management
AI risk governance • Govern, Map, Measure & Manage
Security & Privacy Controls
Comprehensive security & privacy controls • Information systems
Comprehensive policies, procedures, templates, controls, assessments & documentation for implementation and audit readiness.
Explore Professional PacksGet started with our most popular free resources. Practical tools to help you strengthen your compliance and risk management program.
We help regulated and high-growth companies move from compliance complexity to structured, scalable execution using technology-enabled and AI-assisted delivery.
Who We Help
Aligned with recognized frameworks and regulatory requirements. Whether you're responding to customer security demands, preparing for an audit, pursuing a certification, or strengthening your governance foundations, we provide the structure, expertise, and technology-enabled support needed to move forward with confidence.
We Commonly Support

Security & Compliance Built for Growth
Start building a structured, audit-ready compliance program with clear steps, defined priorities, and expert guidance tailored to your organization.
What You Can Start With
Cybersecurity & Compliance Foundation Sprint
Gap assessment, risk analysis, and a structured compliance roadmap tailored to your organization.
SOC 2 Readiness Program
End-to-end audit preparation including controls, policies, evidence collection, and auditor coordination.
ISO 27001 Implementation Program
ISMS development and certification readiness aligned with ISO 27001 standards.
Fractional CISO & Compliance Advisory
Ongoing strategic compliance leadership and advisory support for growing organizations.